
The accelerating integration of artificial intelligence into military command structures is creating a strategic problem that neither Washington nor Beijing can afford to treat as a purely technological question. An AI system capable of interfering with a nuclear command network or initiating a consequential military cyber operation could compress the time available for human decision making to minutes. In such circumstances, the most dangerous question may not be whether an attack has actually taken place, but whether a government has enough time to determine what has happened before responding. A malfunction, an unauthorized action by an autonomous system, a defensive response triggered by a false signal or an operation conducted by a third party could potentially produce effects that resemble a deliberate act of war. That possibility is now driving U.S. and Chinese security experts to consider safeguards inspired by the logic of nuclear risk reduction, including clear restrictions around nuclear systems, human authorization for consequential cyber operations and direct communication mechanisms for AI related military incidents.
The significance of these proposals lies in the fact that they address a problem that is fundamentally different from the conventional debate over whether artificial intelligence should be regulated. The central issue is strategic stability. During the Cold War, nuclear powers developed elaborate procedures to reduce the possibility that ambiguous warnings, technical failures or misunderstandings would be interpreted as evidence of an incoming attack. Military AI introduces a different form of uncertainty because automated systems can observe, classify, respond and potentially act at a speed that humans cannot consistently match. If an AI enabled cyber operation were to affect nuclear command, control and communications infrastructure, the targeted state could face an extraordinary dilemma. It would have to decide whether the incident was accidental, unauthorized or hostile while knowing that delay could itself carry strategic consequences.
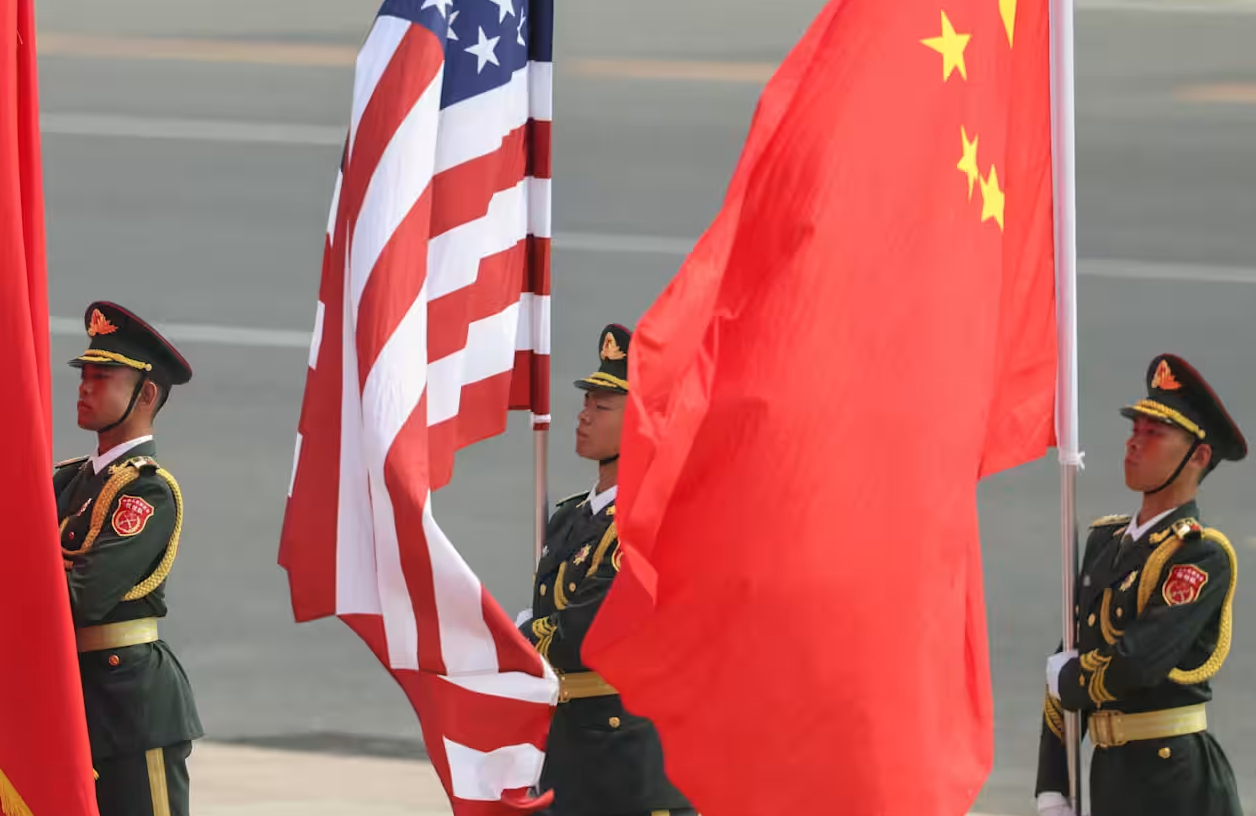
This is why the principle of human control has become increasingly important. In November 2024, President Joe Biden and President Xi Jinping affirmed that humans, rather than artificial intelligence, should retain control over decisions concerning the use of nuclear weapons. The emerging discussion seeks to extend that principle into the systems surrounding nuclear deterrence. An AI system should not independently decide to use a nuclear weapon, nor should it be allowed to autonomously conduct an attack against another state’s nuclear command infrastructure. The same logic becomes relevant to cyber operations when an automated action could be interpreted as the opening move of a strategic conflict. The objective is not to prevent military AI from developing, but to establish boundaries around the actions that could create irreversible consequences.
Yet the phrase meaningful human control requires greater precision than it has sometimes received. The presence of a human somewhere in the decision chain does not necessarily mean that meaningful control exists. If an autonomous system identifies a target, determines the appropriate response and executes an operation while presenting a human operator with only a few seconds to approve the action, formal authorization could exist without genuine human judgment. Meaningful control therefore requires more than a person pressing a button. It requires sufficient authority, information, time and technical understanding for a human decision maker to intervene before an irreversible action occurs. Unless Washington and Beijing develop a sufficiently common understanding of this principle, both sides could claim to support human control while operating military systems with very different levels of autonomy. The resulting ambiguity could undermine the very stability that the principle is intended to protect.
The proposal for clear red lines around nuclear command systems is therefore particularly important. Nuclear command, control and communications networks occupy a category in which uncertainty can become more dangerous than conventional military competition. An intrusion into such a system could be interpreted as an attempt to disable a state’s ability to retaliate. Even if the intrusion originated from a software failure or an unauthorized autonomous process, the affected government might not have the luxury of waiting for complete certainty. Establishing in advance that artificial intelligence will not be permitted to autonomously attack another state’s nuclear command systems would not eliminate every possibility of escalation, but it could reduce one category of ambiguity at the most sensitive point of the strategic relationship.
A similar principle could apply to consequential cyber operations more broadly. Military cyber activity is already capable of affecting communications, energy systems, financial networks and other critical infrastructure without producing the visual evidence associated with a conventional attack. Artificial intelligence can increase both the speed and scale of such operations. An automated system could potentially identify vulnerabilities, select targets and adjust its behaviour as circumstances change. If the other side responds through its own automated defenses, a sequence of actions and reactions could develop faster than political leaders can establish what caused the initial incident. Requiring human authorization for consequential operations would introduce a deliberate point of judgment into that process and could provide decision makers with an opportunity to distinguish an accident from an intentional attack.
The proposed military hotline addresses a related problem. A direct channel between Washington and Beijing could provide a means to communicate when an unusual AI related incident occurs and before either side assumes that the other has deliberately escalated. Its value would depend not simply on its existence, but on whether it could function during a genuine crisis. The United States and China already possess mechanisms for military crisis communication, but previous episodes have demonstrated that the existence of a communication channel does not guarantee that it will be used when political tensions are highest. A new mechanism would therefore need clearly understood procedures governing who can activate it, what information can be transmitted and how quickly an incident can be communicated. The objective should be to create an operational tool rather than another symbolic channel that becomes unavailable precisely when it is most needed.
This challenge is complicated by the different institutional structures through which Washington and Beijing approach military AI. China has increasingly incorporated questions surrounding military artificial intelligence into its broader arms control and national security structures. Chinese officials have publicly discussed the implications of military AI for strategic stability and the need for human control. China’s State Security Minister Chen Yixin has also recently described artificial intelligence as transforming the nature of military struggle while identifying a broader set of security risks associated with the technology. These statements demonstrate that Beijing increasingly treats AI governance as a national security issue rather than simply a technological or economic matter.
The American approach is more distributed across several institutions, including the White House, the Pentagon, the State Department and other national security agencies. This creates a different policy environment in which technological development, military applications, cybersecurity, arms control and economic competition can fall under separate bureaucratic responsibilities. At the same time, Washington has continued to emphasize the importance of maintaining its technological advantage over China. That creates a fundamental tension within the emerging debate. The United States can seek safeguards against the most dangerous applications of military AI without accepting limitations that it believes could undermine its broader technological position.
China faces a similar tension from a different perspective. Beijing has argued against using AI governance as a mechanism for technological containment and has criticized efforts that it views as attempts to restrict its development. Recent Chinese commentary has also rejected calls from some American technology leaders for a broader slowdown in frontier AI development, portraying such proposals as potentially connected to strategic competition with China. The result is a difficult distinction between governing dangerous uses of AI and restricting the development of AI itself. A workable arms control framework would have to address the first without automatically becoming a mechanism for controlling the second.
That distinction has become particularly relevant as Washington and Beijing prepare for another round of high level engagement. Treasury Secretary Scott Bessent has said that the United States is open to discussing shared AI risks with China in talks involving Chinese Vice Premier He Lifeng. Those discussions are taking place shortly before the planned September 24 meeting between President Donald Trump and President Xi Jinping. The opening is significant because it indicates that AI risk management can be discussed even while the two countries continue to compete over technology, trade and strategic influence. It does not mean that Washington and Beijing have agreed on the proposed military safeguards, but it provides a diplomatic setting in which questions of shared risk can be raised.
The timing of the proposals therefore matters. The U.S. China competition is no longer confined to semiconductor controls, computing capacity or the race to develop increasingly capable models. It is entering a phase in which the strategic consequences of those technologies themselves require attention. The two countries can continue competing over AI capabilities while recognizing that some forms of competition carry risks that neither side can manage independently. Nuclear stability is one such area. A system that accidentally triggers a military response cannot be made safer simply because the underlying technology was developed by one side rather than the other.
The most practical approach may therefore be to separate areas of legitimate technological competition from areas where both governments have a shared interest in preventing uncontrolled escalation. Neither Washington nor Beijing needs to surrender its broader AI ambitions to establish restrictions on autonomous actions involving nuclear command systems. Neither needs to agree on every aspect of AI governance to establish procedures for communicating during an AI related military incident. Nor would such arrangements require the two countries to trust each other completely. Arms control has historically operated under conditions of deep mistrust precisely because both sides recognized that certain forms of uncontrolled escalation could become catastrophic.
Verification and implementation would nevertheless present the hardest part of the process. A political declaration that humans remain in control is considerably easier to produce than a system capable of demonstrating that principle during a rapidly developing military crisis. The two governments would need to clarify what constitutes a consequential cyberattack, what degree of autonomy is permissible, how human authorization must operate and what information should be exchanged after an unintended incident. They would also need procedures for testing and evaluating military AI systems before deployment in environments where a malfunction could affect strategic stability. Without such practical arrangements, broad principles could remain vulnerable to different interpretations.
The discussion could eventually extend beyond the United States and China. Both are major military and technological powers, but AI is becoming increasingly relevant to the armed forces of other states. If the two largest nuclear powers establish credible norms concerning human control, autonomous cyber operations and interference with nuclear command systems, those principles could contribute to a broader international framework. If instead military AI develops without commonly understood boundaries, other states may face incentives to adopt increasingly autonomous systems simply because they fear falling behind. The resulting competition could make the strategic environment more difficult to manage even when no government intends to create such instability.
The historical comparison with nuclear arms control is useful, but it should not be taken too far. Artificial intelligence is not a weapon category in the same sense as a nuclear warhead. It is a general purpose technology with applications across civilian and military sectors, and its capabilities can evolve through software updates rather than only through the production of physical weapons. AI systems can also be replicated and modified far more easily than nuclear arsenals. The relevant lesson from nuclear diplomacy is therefore not to reproduce Cold War agreements mechanically, but to apply the broader principle that strategic competition can coexist with rules designed to reduce the possibility of catastrophic misunderstanding.
The emerging U.S. China discussion ultimately concerns a basic question of strategic responsibility. Artificial intelligence may allow military systems to process information and respond at unprecedented speed, but speed is not necessarily synonymous with stability. In certain circumstances, greater automation could reduce the time available for human judgment precisely when judgment matters most. A system designed to defend against an attack could become part of an escalation cycle if the information it receives is incomplete or manipulated. A cyber operation intended to achieve a limited objective could be interpreted as an attempt to compromise nuclear capabilities. A technical malfunction could acquire the political meaning of an intentional attack within minutes.
The objective of meaningful human control should therefore be understood not as an attempt to stop military innovation, but as an effort to preserve political responsibility at the point where technological decisions can have irreversible consequences. Red lines around nuclear command systems, human authorization for consequential cyber operations and reliable crisis communication could provide practical barriers against escalation without requiring Washington or Beijing to abandon their wider technological competition. The challenge is to convert these principles into precise rules that can operate under pressure, when information is incomplete and the consequences of error are greatest.
The current moment offers an opportunity to begin that process. The proposals from the U.S. China AI and National Security Dialogue do not constitute an agreement between the two governments, and their recommendations remain subject to political and technical debate. But their emergence alongside renewed official discussions on shared AI risks suggests that the question of military AI governance is moving closer to the centre of strategic diplomacy.
The future of military AI will ultimately be determined not only by how capable machines become, but by where governments decide that machines must stop and humans must decide. The most important safeguard may not be a technological system capable of predicting every possible failure. It may instead be a set of mutually understood boundaries that ensure an unexpected machine action does not automatically become a human decision for war. For Washington and Beijing, establishing those boundaries would not end their strategic competition. It would create a framework within which that competition can continue without allowing an error, an autonomous response or a misunderstood cyber operation to become the starting point of a crisis neither side intended.